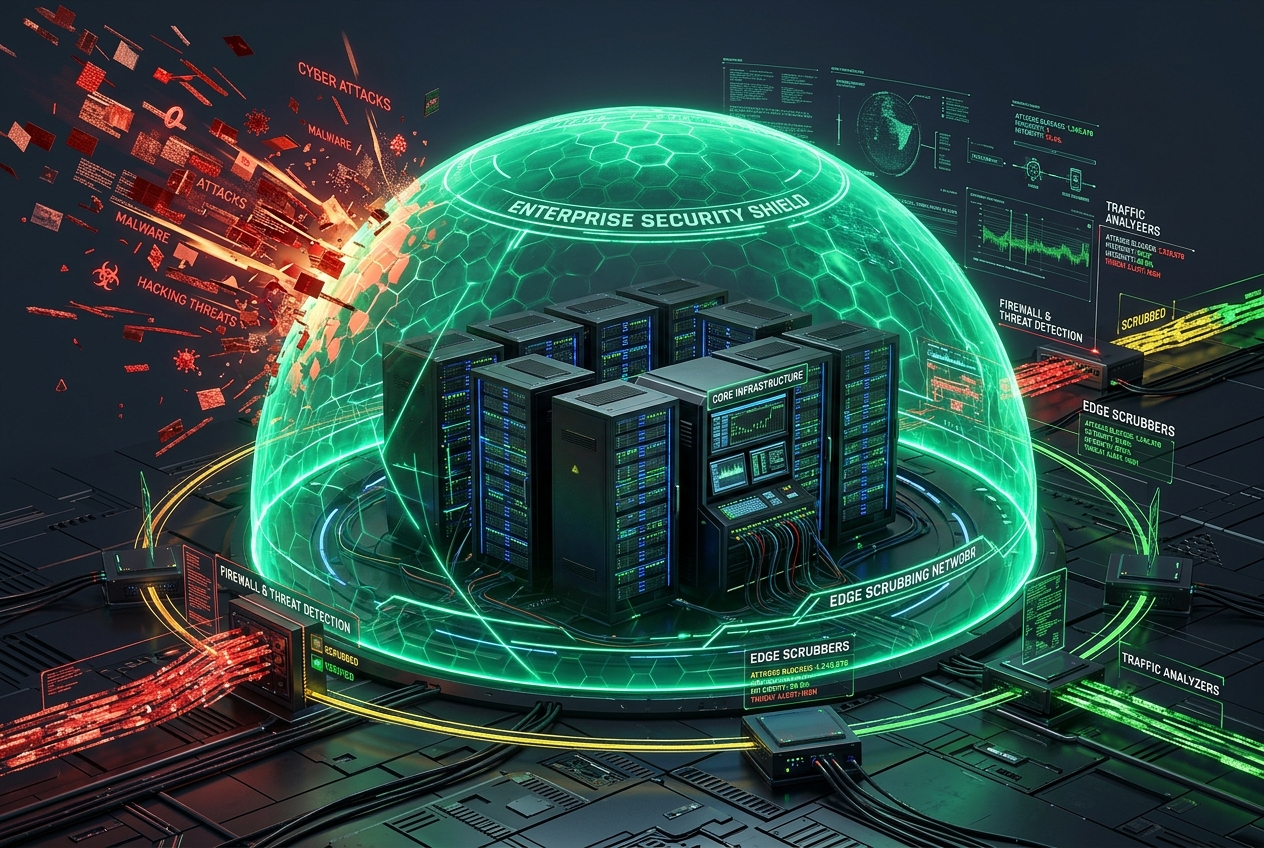
- •BGP Anycast Edge Scrubbing: Ingest attack traffic across distributed Point of Presence (PoP) edge routers before it ever reaches server ports.
- •SYN Cookie Offloading: Protect Linux kernel memory buffers from exhaustion during 50M+ pps TCP SYN floods.
- •Layer 7 Dynamic Rate Limiting: Block automated bot scrapers and HTTP/2 rapid reset attacks without penalizing legitimate user checkouts.
The Anatomy of Modern DDoS Attacks
Modern distributed denial-of-service attacks have evolved beyond simple volumetric UDP amplification. Attackers now orchestrate multi-vector campaigns combining Layer 3/4 network saturation with precision Layer 7 HTTP floods designed to exhaust database connection pools.
Edge Scrubbing vs Origin Server Protection
Attempting to filter multi-gigabit DDoS traffic at the origin server's software firewall is a recipe for disaster: network interface cards (NICs) become saturated, and CPU interrupts consume 100% of server capacity. At Clouds Panel, incoming traffic routes through BGP Anycast edge nodes equipped with hardware scrubbing filters that inspect and drop malicious packets in silicon at sub-microsecond line rates.
Kernel-Level TCP Hardening in sysctl.conf
To defend against local SYN floods and network starvation, deploy these optimized kernel parameters in /etc/sysctl.conf:
# Enable SYN Cookies to prevent SYN queue exhaustion
net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_max_syn_backlog = 8192
net.ipv4.tcp_synack_retries = 2

# Drop spoofed source IP packets
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1

# Ignore ICMP echo broadcasts
net.ipv4.icmp_echo_ignore_broadcasts = 1

# Increase connection tracking limits
net.netfilter.nf_conntrack_max = 1048576
Nginx Layer 7 Rate-Limiting & Mitigation
For API endpoints and login routes, rate-limiting prevents bad actors from creating synthetic bottlenecks:
# Allocate 20MB shared zone tracking client IPs
limit_req_zone $binary_remote_addr zone=api_limit:20m rate=30r/s;

server {
    location /api/ {
        limit_req zone=api_limit burst=15 nodelay;
        limit_req_status 429;
        proxy_pass http://backend_upstream;
    }
}
Security Guarantee
Every server provisioned on Clouds Panel comes with standard hardware-level DDoS protection up to 100Gbps, mitigating attacks upstream before packet floods touch your virtual machine interface.